2 August 2026 was an important date for the European Union’s Artificial Intelligence Act. Yet treating it as proof that every AI obligation now applies in exactly the same way creates rushed decisions: unnecessary purchases, generic policies, and teams documenting everything without knowing which risk they are actually managing.
A more useful reading is that the AI Act has a phased timetable. Some obligations started earlier; from August 2026, specific transparency requirements and enforcement powers become particularly relevant. By contrast, obligations for many high-risk systems have later dates: 2 December 2027 for Annex III use cases and 2 August 2028 for systems embedded in regulated products. The European Commission sets out this sequence in its AI Act enforcement framework.
Responsible preparation is not about chasing a date. It is about knowing what system is used, what decision it supports, and who can intervene when something goes wrong.
Change the question: from “we use AI” to “we know how it operates”
An organisation may use AI in many different ways: a website chatbot, draft generation, enquiry classification, transcription, campaign support, document analysis, or internal recommendations. Those uses do not carry the same impact, nor do they require identical controls.
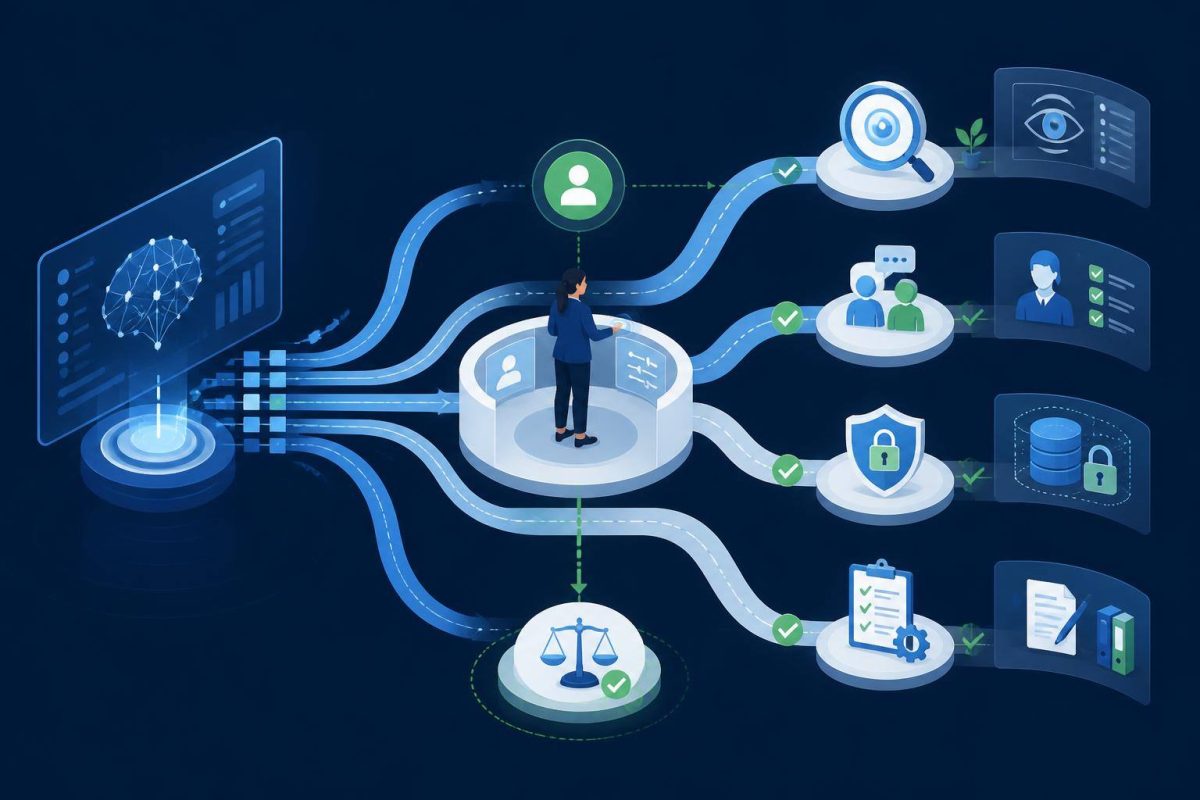
That is why the first deliverable should not be a public statement or a long policy. It should be a short, living inventory. For every use, record the provider, purpose, users, data received, output produced, whether a person reviews it, and what happens when the output is wrong.
What is worth reviewing now
The transparency rules that began to apply on 2 August 2026 make the experience of people interacting with a system especially important. The Commission states that people must be informed in certain cases when they are interacting with AI. It also sets out marking or labelling duties for generated or manipulated content and notices for certain exposure to synthetic content. The Commission’s transparency guidance helps distinguish the responsibilities of providers and organisations deploying systems.
- Interaction: check whether a conversational assistant clearly identifies itself as automated where required.
- Content: define a process for identifying synthetic material, especially where it could mislead people about individuals, facts, or official messages.
- Human review: specify which outputs need approval before publication, delivery, or conversion into an operational action.
- Correction route: provide a simple way to request human help, report an incorrect answer, or challenge an outcome.
- Evidence: retain versions of instructions, approved sources, tests, and meaningful changes.
Why waiting for 2027 or 2028 is not a strategy
Later deadlines for some high-risk obligations are not a reason to ignore the issue. They are an opportunity to prepare operations without improvisation. When a system contributes to sensitive areas—such as employment, education, access to services, or decisions with significant effects on people—the cost of finding a wrong classification or missing control too late can be substantial.
The legal text available through EUR-Lex should be read alongside the actual use case and any sectoral, data-protection, and consumer rules that may also apply. This article is not legal advice. It offers an operational way to arrive at that assessment with organised information.
A 60-day plan that avoids empty paperwork
- Weeks 1–2: collect every AI use case, including tools acquired by teams without direct technology involvement.
- Weeks 3–4: separate internal support uses from systems affecting customers, applicants, students, users, or material decisions.
- Weeks 5–6: test error, bias, hallucination, unauthorised data access, and lack-of-escalation scenarios.
- Weeks 7–8: assign owners, define concrete changes, and document decisions—including reasons not to automate a task.
The practical decision
The August 2026 milestone does not mean every organisation must turn every tool into a complex compliance project. It does mean that improvisation is no longer enough. Start with transparency, inventory, usage limits, and the ability to correct mistakes. Then go deeper where a system has greater autonomy, handles more sensitive data, or influences decisions with real consequences.
If you need to turn that inventory into workflows, integrations, permissions, testing, and operational oversight, explore our artificial intelligence solutions. The starting point is not “add AI”; it is solving a specific task with controls your team can maintain.